

Expanded Attack Surface
Remote work and the rise of unmanaged cloud services (Shadow IT) significantly increase the number of potential entry points for attackers.

Modern enterprises face a growing security challenge driven by changes in how they operate. This results in several critical issues:
Remote work and the rise of unmanaged cloud services (Shadow IT) significantly increase the number of potential entry points for attackers.
Traditional VPN-based access grants broad network access after authentication, enabling attackers to move laterally once inside the network. A single compromised credential can expose large portions of the internal network due to lack of granular access controls.
Backhauling all remote traffic through a central datacenter for security inspection creates congestion and latency. High latency and poor application performance frustrate users and negatively impact day-to-day work efficiency.
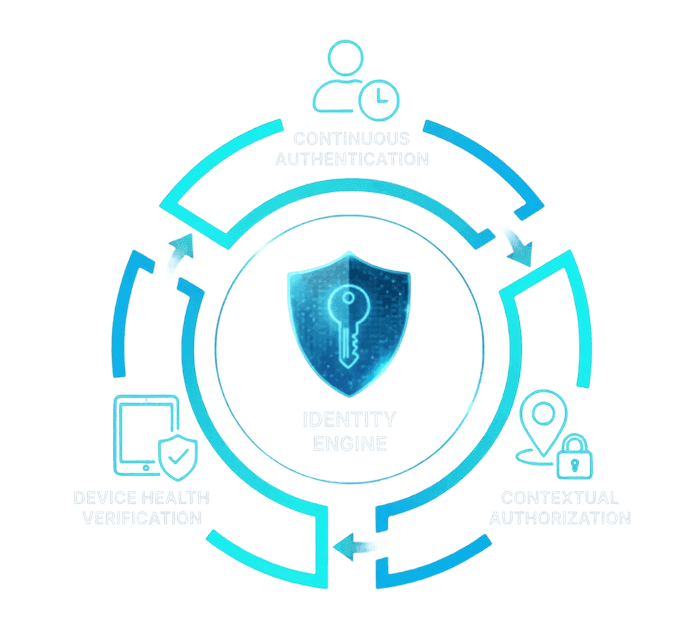
We address these challenges by re-architecting security at the "edge." By moving from perimeter-based security to zero-trust resilience, we ensures that every access request is continuously authenticated and authorized based on user identity, device health, and location.
This approach reduces the attack surface while improving visibility and control, ensuring that compromise in one segment does not automatically spread across the organization.
We address these challenges by re-architecting security at the "edge." By moving from perimeter-based security to zero-trust resilience, we ensures that every access request is continuously authenticated and authorized based on user identity, device health, and location.
This approach reduces the attack surface while improving visibility and control, ensuring that compromise in one segment does not automatically spread across the organization.
UpArrow's edge security strategy is delivered through the Secure Access Service Edge (SASE) model, which converges networking and security into a single cloud-delivered platform.
Replaces traditional VPNs by providing secure, granular access to specific applications rather than the entire network.
Filters malicious web traffic and enforces corporate policies for users regardless of their location.
Provides visibility and control over data residing in SaaS applications, preventing unauthorized data uploads or leaks.
Enforces high-performance segmentation and threat filtering at both the network edge and within cloud environments.
Technology is only half the battle. UpArrow provides the human expertise and processes to act on the data:
Education and research institutions utilize ZTNA to provide secure access to vast networks of students and researchers without exposing sensitive intellectual property.
In the Energy sector, Zero Trust is applied to Operational Technology (OT) networks, ensuring that only authorized personnel can access critical control systems for oil refineries or power grids.
Retailers use SASE to securely connect distributed point-of-sale (POS) systems directly to the cloud, bypassing the need for expensive and slow backhaul links.
UpArrow Systems stands out by delivering "Zero Compromise" infrastructure that aligns with business agility. By adopting a SASE model, we reduces the complexity and cost of managing multiple point products, cutting hardware expenses and administrative overhead. Clients benefit from a consistent security posture where the same access policies apply to all users, whether they are in the office or remote, ensuring that digital transformation does not come at the cost of security integrity.


