

The Visibility Gap:
Security teams miss breaches because they look like performance glitches, and network teams ignore anomalies that are actually cyberattacks.

Many organizations suffer from "fragmented visibility," where network and security teams work in silos. This leads to several critical issues:
Security teams miss breaches because they look like performance glitches, and network teams ignore anomalies that are actually cyberattacks.
Managing millions of events per second makes it nearly impossible for analysts to find real threats.
Maintaining 24/7 coverage is difficult due to the global lack of specialized security experts.
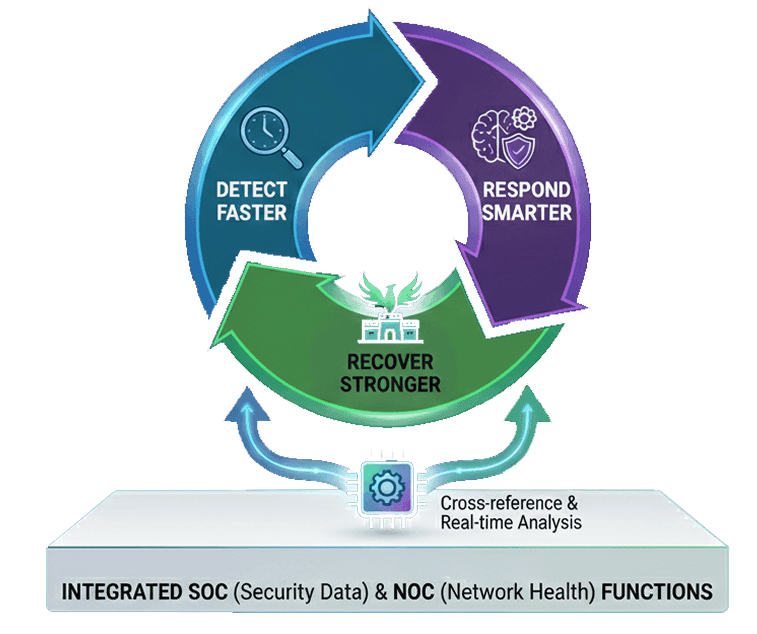
INTEGRATED SOC (Security) & NOC (Network Health) FUNCTIONS
We move the conversation from the cost of monitoring tools to the value of risk reduction and peace of mind.
We solves these challenges by implementing a "Detect Faster, Respond Smarter, Recover Stronger" methodology.
By integrating integrating SOC and NOC functions, we cross-reference network health with security data in real-time, significantly reducing dwell time, the period an attacker remains undetected within a network.
We move the conversation from the cost of monitoring tools to the value of risk reduction and peace of mind.
We solves these challenges by implementing a "Detect Faster, Respond Smarter, Recover Stronger" methodology.
INTEGRATED SOC (Security) & NOC (Network Health) FUNCTIONS
By integrating integrating SOC and NOC functions, we cross-reference network health with security data in real-time, significantly reducing dwell time, the period an attacker remains undetected within a network.
We use enterprise-grade tools to provide a "single pane of glass" view of your entire digital environment.
Centralized log management and correlation engines (e.g., Splunk, QRadar) that provides a pattern in the security data.
Advanced telemetry collection from endpoints, networks, and cloud workloads that uses automated correlation to reveal complex attack sequences.
Continuous ingestion of global threat feeds to map internal activity against known malicious IPs, domains, and file hashes
Technology is only half the battle. UpArrow provides the human expertise and processes to act on the data
In the Financial/Banking sector (BFSI), this unified monitoring is critical for protecting high-speed trading links and detecting transaction fraud in real-time.
Real-time visibility ensures the integrity of ground-to-air communication, protects airport operational infrastructure (baggage handling, fuel systems), and secures the supply chain for aircraft maintenance data against ransomware.
For the Healthcare sector, continuous monitoring ensures the integrity of patient record systems and the availability of life-saving medical devices.
Selecting UpArrow Systems for monitoring means partnering with an organization that treats security as a "continuous journey" rather than a one-off product purchase. UpArrow's unified SOC/NOC approach has shown to improve response times and reduce operational costs by removing redundant tools and teams. Furthermore, UpArrow's focus on communication ensures that clients are briefed regularly on their security posture, transitioning the service from a "black box" to a reliable extension of the in-house team.


